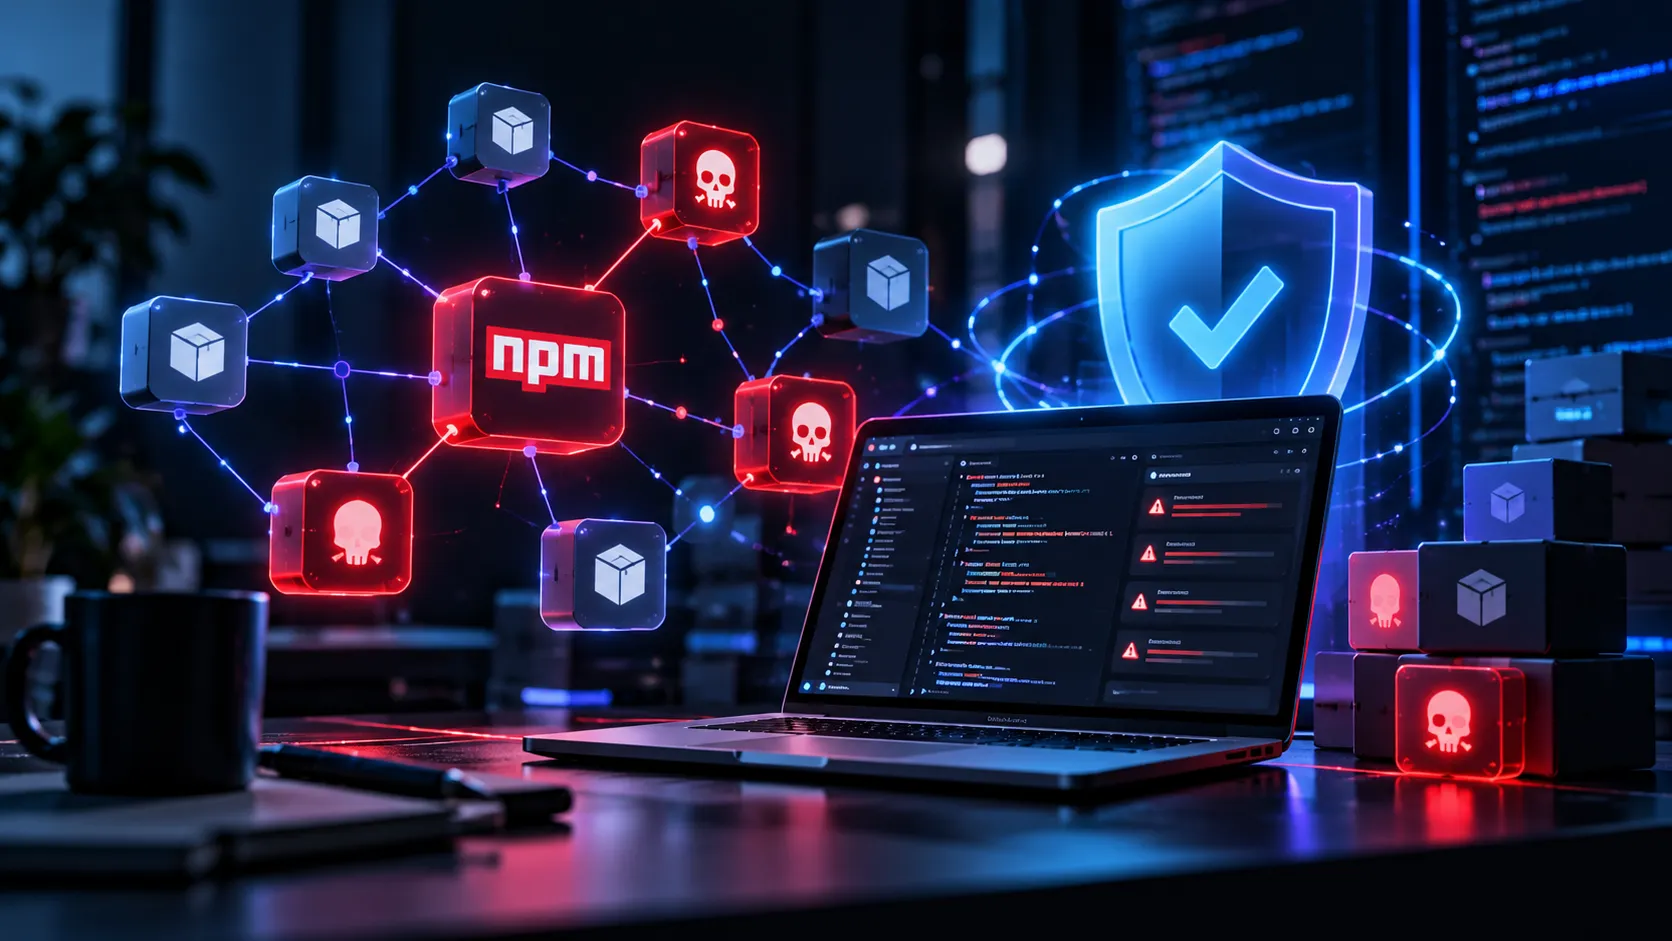
Technology News Today: npm Malware Advisories, Critical Vulnerabilities and Supply-Chain Security
Date: October 5, 2026
Coverage: October 4–5, 2026
Focus: JavaScript, TypeScript, Node.js, npm, supply-chain security, developer tools and AI
Introduction
Today's package deliberately avoids recycling older stories. The main developer story for October 5 is not a new major JavaScript runtime release; it is a fresh wave of dependency-security advisories in the npm ecosystem.
GitHub Advisory Database lists multiple new npm advisories classified as Malware, including focus-visible-polyfill-lite, css-anchor-pos-fallback, css-reading-flow-polyfill, css-snap-target-polyfill, chai-as-testmode, express-enhanced, and core-js-gnz. These should not automatically be treated as one coordinated incident: the advisories are package-specific and many are currently Unreviewed.
Two Critical Legcord vulnerabilities were also published for versions 1.1.0 through 1.3.0, while GitAhead 2.5.0 through 2.7.1 has a High-severity insecure update mechanism issue.
Quick Take
- 🔴 Multiple new npm Malware advisories were published on October 5.
- 🔴 Legcord 1.1.0–1.3.0:
CVE-2026-105293andCVE-2026-105294, both Critical. - 🟠 GitAhead 2.5.0–2.7.1:
CVE-2026-105295, High. - 🟢 No qualifying fresh Node.js, Deno or Bun release was found.
- 🟢 No major fresh Chrome, Firefox or WebKit announcement was found.
- 🟡 Today's dominant developer theme is dependency and supply-chain security.
1. New npm Malware Advisories
Date: October 5, 2026
Status: Security Advisory / Unreviewed
GitHub Advisory Database currently lists a batch of new npm advisories classified as Malware. Examples include:
focus-visible-polyfill-litecss-anchor-pos-fallbackcss-reading-flow-polyfillcss-snap-target-polyfillchai-as-testmodeexpress-enhancedcore-js-gnzcss-a11y-contrast-utilscss-scroll-anchor-polyfillcss-logical-prop-shimcss-field-sizing-polyfillcss-interop-observer-polyfillcss-scroll-state-polyfillcss-env-function-shimcss-relative-color-utilcss-gap-decorations-polyfillcss-light-dark-polyfillcss-starting-style-polyfillexpress-forkhardhat-jsxmonitoring-agent
A malware advisory for a package does not automatically mean every version or every consuming project is compromised. Check the exact affected and fixed versions in the relevant advisory.
Why it matters
A small transitive dependency can reach developer machines, CI runners, build systems and production environments.
Recommended action
npm audit
npm outdated
npm ls --depth=0
For a suspicious package, inspect the lockfile and installation history before changing dependencies. Do not blindly run npm update.
Primary source: https://github.com/advisories?query=type%3Amalware
2. Two Critical Legcord Vulnerabilities
Date: October 5, 2026
Severity: Critical
CVEs: CVE-2026-105293, CVE-2026-105294
GitHub lists two Critical advisories affecting Legcord 1.1.0 through 1.3.0.
CVE-2026-105293 concerns path traversal in theme IPC handlers.
CVE-2026-105294 describes configuration injection allowing script execution.
Both are currently shown as Unreviewed in GitHub's database, so the advisory status should be distinguished from a fully reviewed final analysis.
If Legcord is installed on developer workstations or organizational systems, check the installed version and follow the advisory guidance.
Primary source: https://github.com/advisories?query=severity%3Acritical
3. GitAhead's Insecure Update Mechanism
Date: October 5, 2026
Severity: High
CVE: CVE-2026-105295
GitAhead 2.5.0 through 2.7.1 is affected by an insecure update mechanism.
Updater security matters particularly for desktop developer tools because update processes may operate with elevated privileges.
Primary source: https://github.com/advisories?query=sort%3Aupdated-desc
4. JavaScript, TypeScript and Runtime Status
Node.js
No qualifying Node.js release was found inside today's strict window. Node.js 26.10.0 is dated September 22, 2026 and is therefore intentionally excluded from today's fresh-news list.
Node.js is still moving toward a one-major-release-per-year model starting with the 27.x line, with an Alpha phase planned for October 2026.
Deno
Deno's official blog lists Deno 2.9 from June 25, 2026 as its latest notable product update. No new Deno release qualified for today's window.
Bun
No fresh official Bun announcement meeting today's criteria was found.
TypeScript and ECMAScript
No fresh TypeScript or TC39 announcement meeting today's criteria was found.
5. Browser and Web Platform
No major fresh Chrome, Firefox or WebKit announcement qualified for today's strict window.
WebKit does publish daily builds, but a daily build should not be presented as a public product release.
Source: https://webkit.org/build-archives/
6. AI and Developer Tools
Older announcements were deliberately excluded. OpenAI's DevDay 2026 announcements, for example, were published on September 29 and therefore fall outside today's 24-hour window.
7. Rumors
No fresh JavaScript/Node.js/TypeScript rumor with enough verification value to publish as a standalone story was found in the coverage window.
FAQ
Does this mean npm was hacked again?
Not necessarily. What is confirmed is that GitHub published multiple new npm advisories classified as Malware on October 5. Each package and affected version should be reviewed independently.
Should I delete all dependencies?
No. Start with the lockfile, dependency tree and exact advisory. Blind removal can break builds.
Is npm audit enough?
No. It is useful, but supply-chain review should also consider GitHub advisories, lockfiles, package provenance and dependency history.
Are all Legcord versions affected?
The advisories published today specify versions 1.1.0 through 1.3.0.
Did Node.js release a new version today?
No qualifying release was found in the strict window. 26.10.0 is from September 22.
Three Priority Actions
1. Audit Node.js dependencies and inspect newly flagged npm packages.
2. Check Legcord 1.1.0–1.3.0 and GitAhead 2.5.0–2.7.1 on your systems.
3. Strengthen lockfile and dependency review for sensitive projects.
Primary Sources
- https://github.com/advisories?query=type%3Amalware
- https://github.com/advisories?query=severity%3Acritical
- https://github.com/advisories?query=sort%3Aupdated-desc
- https://nodejs.org/en/blog/release/
- https://deno.com/blog
- https://webkit.org/build-archives/
- https://developers.openai.com/api/docs/changelog
Related articles
Comments & rating
Share your experience or reply to an existing discussion.
0 comments